SOLUTIONS
Cipherscan for federal suppliers and contractors
Get PQC exposure data you can present to leadership now, without waiting on a full compliance program. Cipherscan scans your TLS services and reports which algorithms they negotiate today, so you can stay ahead of CNSA 2.0's 2027 acquisition requirement for new National Security Systems before a customer audit forces the issue.
ACQUISITION TIMELINE
TODAY
2027
Identify TLS cryptography that may affect your CNSA 2.0 preparation. Cipherscan checks the TLS services you run against the algorithms CNSA 2.0 requires, ML-KEM (FIPS 203) for key exchange and ML-DSA (FIPS 204) for signatures, and flags which hosts still rely on classical cryptography, before the January 1, 2027 acquisition deadline or a customer audit forces the question.
Which federal requirements does this map to?
CNSA 2.0 requires new National Security System acquisitions to be compliant starting January 1, 2027, with existing equipment phased in through 2030 and 2031. A June 2026 Department of War strategy separately proposes adding PQC requirements to CMMC, with a December 31, 2031 deadline for DoW systems. See CNSA 2.0 and Federal PQC Requirements for the full detail on each.
What you get
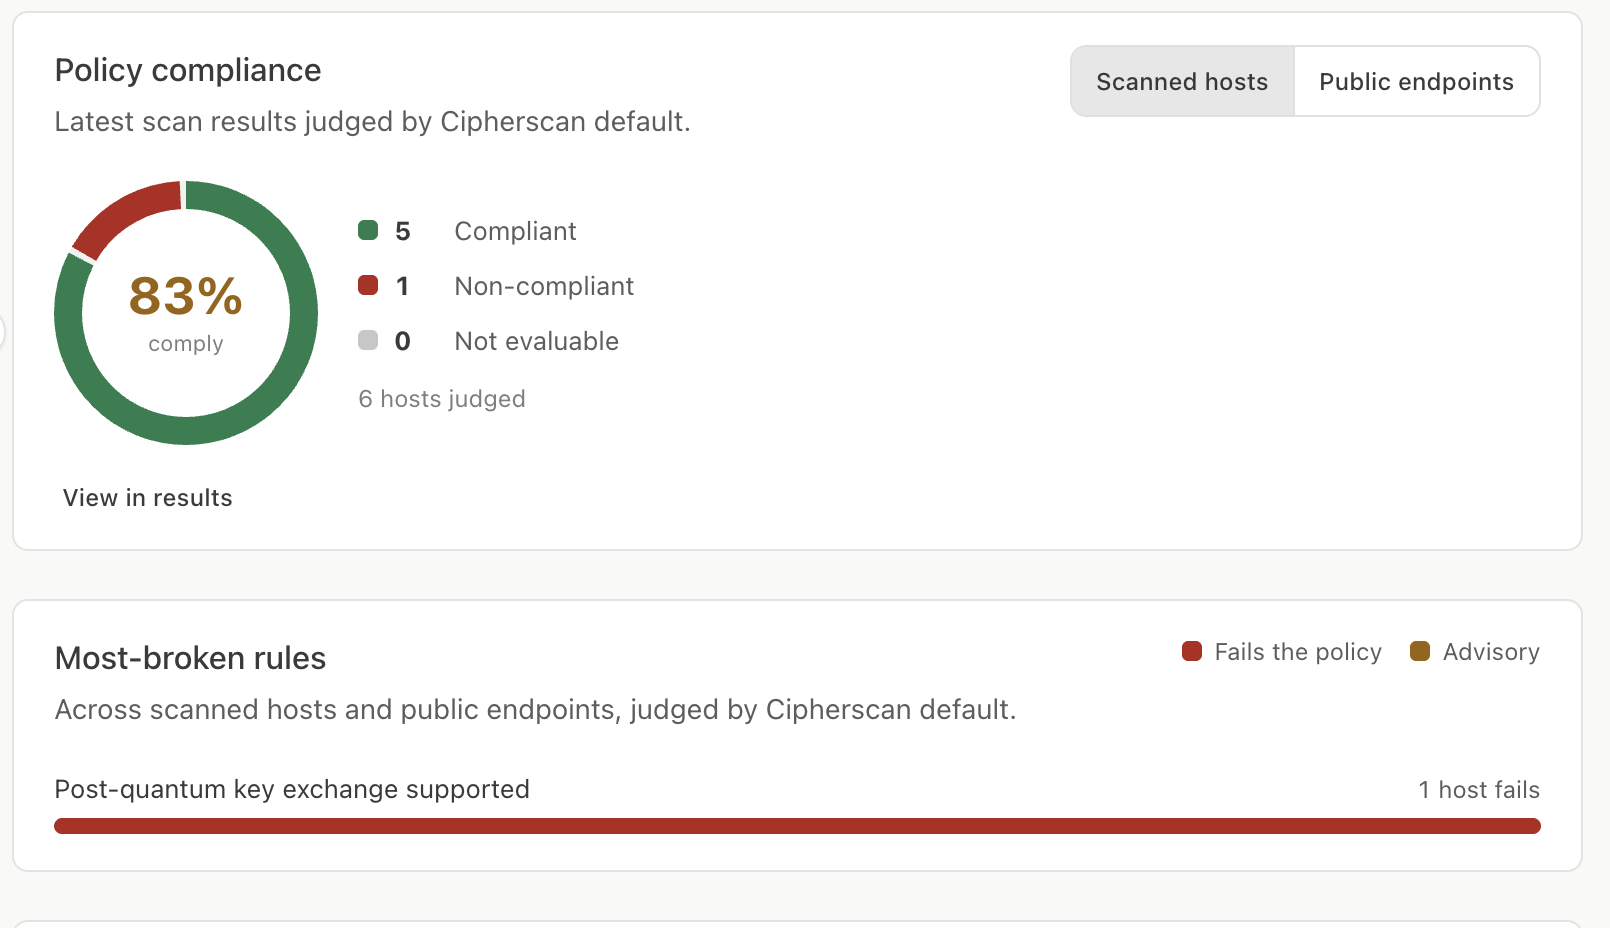
A readiness score you can bring to leadership
One overall percentage backed by real scan results, not a self-assessment questionnaire.
Per-host detail for your engineers
Which specific algorithm each host negotiates, so remediation work has a clear starting point.
Coverage for public and private infrastructure
Hosted scanning for public domains, plus the CLI for systems that aren’t publicly reachable.
Does a Cipherscan scan satisfy a CNSA 2.0 or CMMC requirement?
No. Cipherscan is a cryptographic posture assessment and PQC discovery tool, not a compliance audit or certification body. A scan tells you which algorithms your TLS services negotiate today; it doesn’t itself certify CNSA 2.0 or CMMC compliance, but it gives compliance teams the evidence base they need to plan for either.
Check a domain before you talk to procurement.
Written by the team behind Anvil Secure.